Splunk HEC Logs
Splunk HEC Logs Sink
The Splunk HEC Logs sink can deliver events to a Splunk HTTP Event Collector endpoint.
Configure the general sink settings including any TLS settings, then specify the Splunk HEC Logs specific settings below.
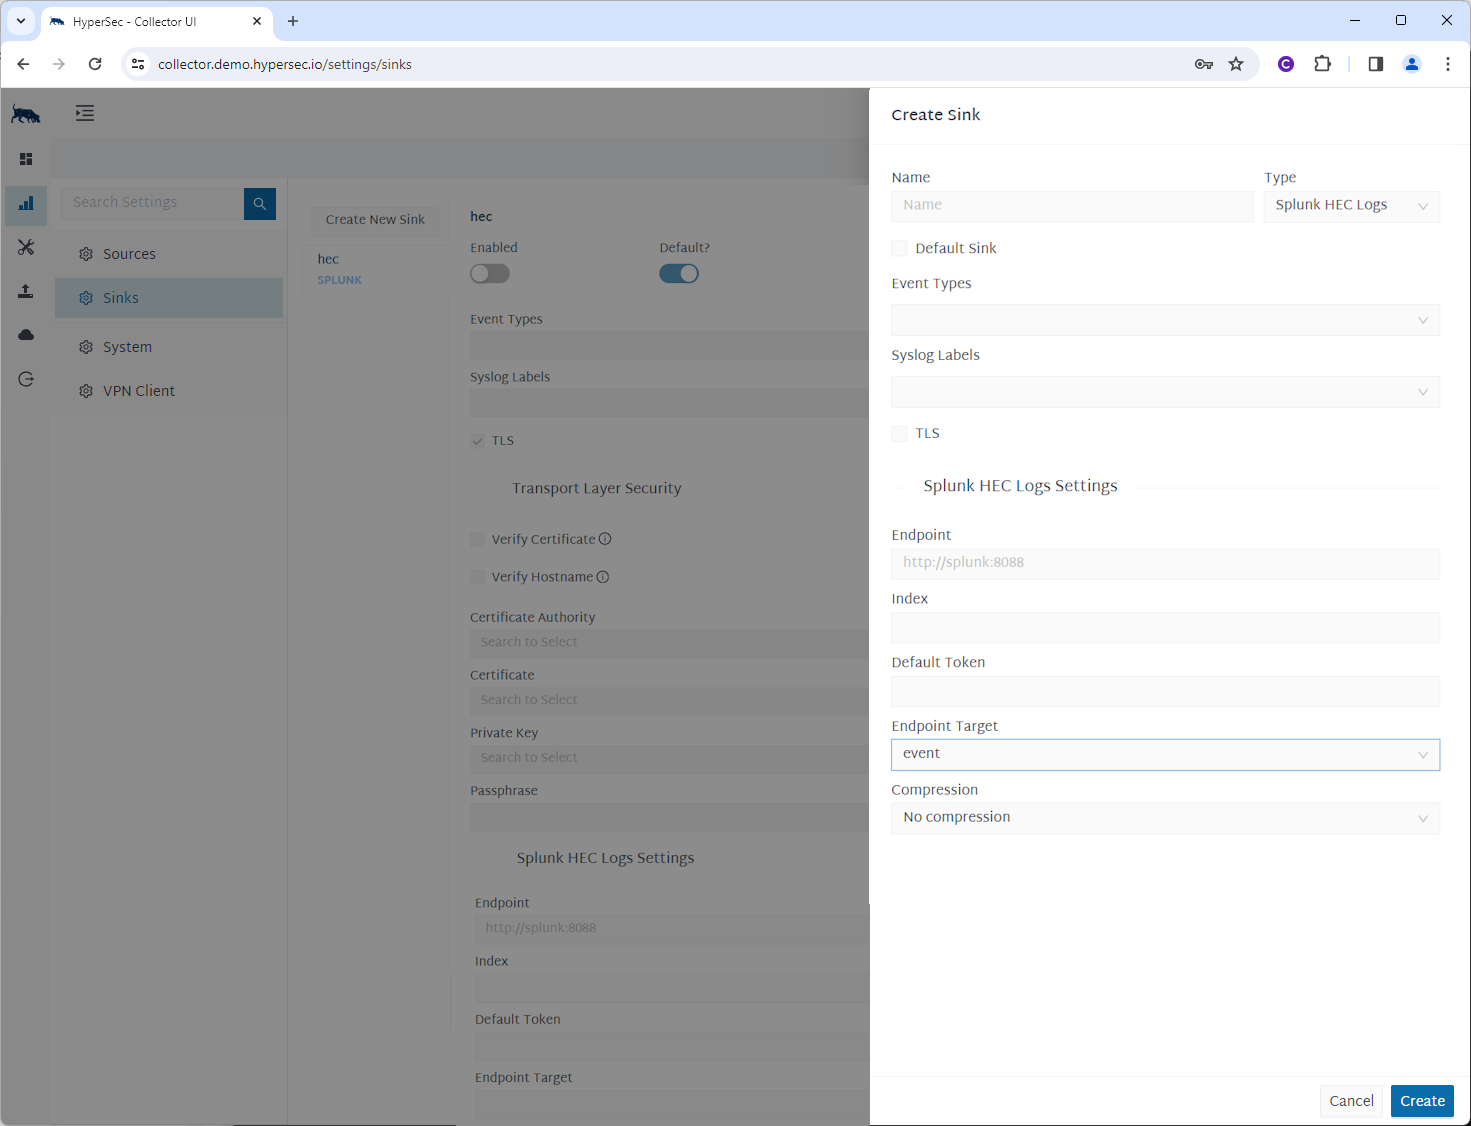
Splunk HEC Logs Sink Settings
Endpoint
Specify the base URL of the Splunk destination HEC endpoint.
The scheme (http or https) must be specified. No path should be included since the paths defined by the Splunk API are used. e.g.:
- https://http-inputs-hec.splunkcloud.com
- https://hec.splunk.com:8088
- https://192.168.1.100:6000
- http://192.168.1.100
Index
The name of the index to send events to.
If not specified, the default index defined within Splunk is used.
Default Token
Default Splunk HEC token.
Endpoint Target
Splunk HEC endpoint configuration.
- event - Events are sent to the event endpoint.\ When the event endpoint is used, configured event metadata is sent directly with each event.
- raw - Events are sent to the raw endpoint.\ When the raw endpoint is used, configured event metadata is sent as query parameters on the request, except for the timestamp field.
Compression
Compression configuration.